Related: Security Consulting & Assessment →Embed automated static, dynamic, and dependency security scanners directly into build pipelines, preventing high severity vulnerabilities from reaching production.
OutcomeEmbed automated static, dynamic, and dependency security scanners directly into build pipelines, preventing high severity vulnerabilities from reaching production.
1Assess
Open-source dependencies and application changes can introduce known vulnerabilities.
2Plan
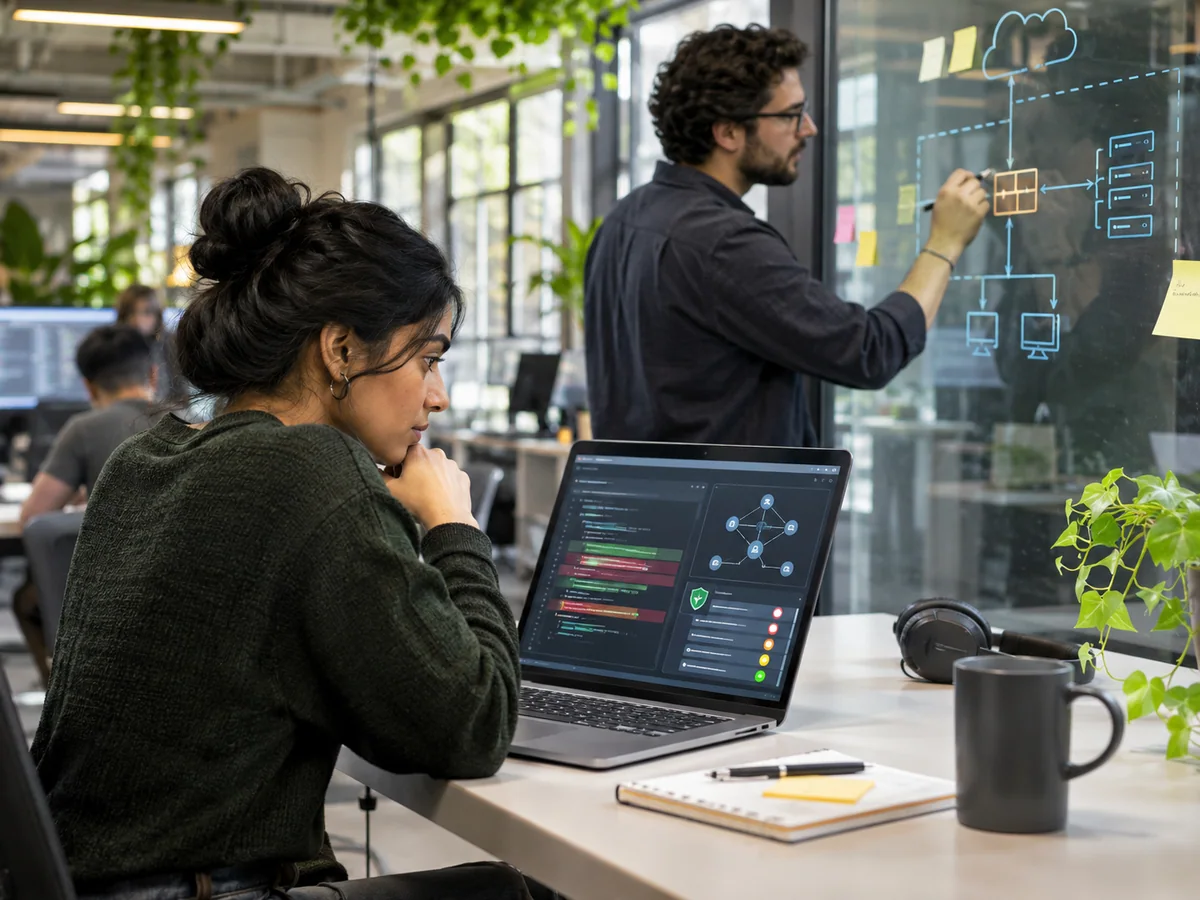
Embed automated SAST, DAST, and SCA vulnerability scanning directly into GitHub Actions, GitLab CI, and Jenkins build pipelines.
3Apply
Embed automated static, dynamic, and dependency security scanners directly into build pipelines, preventing high severity vulnerabilities from reaching production.
4Review
Map applications, infrastructure, repositories, and delivery tools in scope.