preloader

Cybersecurity Services

Vulnerability Assessment & Penetration Testing (VAPT)

Find weaknesses before attackers do. Our vulnerability assessment and penetration testing services cover applications, APIs, cloud environments, and networks, with clear findings your teams can use.

Web and API penetration testing

Test applications for security weaknesses and practical attack paths.

Cloud and infrastructure assessment

Review cloud, network, and container environments for exposure.

Actionable remediation guidance

Give your developers clear findings and steps to address them.

Security pressures

The VAPT Reality: Automated Scans vs. SNWN Ethical Hacking

Security teams need a clear view of risk, a practical response, and improvements that work with their current systems.

Business growth
Fragmented systems
Operational strain
Pressure point 01

Business Logic Flaws

Automated tools can produce long lists without showing which findings are exploitable.

Operational impact
This can make it harder to agree on priorities and move work forward.
How SNWN responds
Our testers validate important findings and explain realistic attack paths.
Pressure point 02

False Positive Overload

Teams need help choosing which vulnerabilities to fix first.

Operational impact
The added handoffs can slow investigation and delay important decisions.
How SNWN responds
We rank findings by severity, exposure, and impact, then provide practical fix guidance.
Pressure point 03

API & Microservices Sprawl

A fix may miss the root cause or affect another feature.

Operational impact
Teams may spend time reviewing noise while key risks remain unresolved.
How SNWN responds
We retest agreed changes and clarify any remaining risk with your team.
Pressure point 04

Internal Lateral Movement

Perimeter-only port scans ignore what happens after an initial workstation compromise or rogue insider foothold.

Operational impact
Without a clear owner, follow-up actions can be difficult to track.
How SNWN responds
Adversary Simulation: We simulate realistic internal breach scenarios, demonstrating Active Directory credential harvesting, lateral pivot, and domain takeover.

Core security capabilities

Core VAPT & Security Testing Capabilities

Select the capabilities that fit your environment, current risks, and internal team needs.

ApplicationsCustomer and business tools
IntegrationAPIs and workflows
Cloud platformSecure foundations
Reliable operationsObserve and improve
Capability 01

1. Web Application Penetration Testing

Perform manual and automated penetration testing across web apps and SaaS platforms to uncover OWASP Top 10 and logic flaws.

Practical deliverables

  • Perform manual and automated penetration testing across web apps and SaaS platforms to uncover OWASP Top 10 and logic flaws.
Capability 02

2. Mobile Application Security Testing (MAST)

Conduct static and dynamic security assessments of iOS and Android applications against OWASP MASTG standards, binary protections, and APIs.

Practical deliverables

  • Conduct static and dynamic security assessments of iOS and Android applications against OWASP MASTG standards, binary protections, and APIs.
Capability 03

3. API & Microservices Security Testing

Audit REST, GraphQL, and gRPC endpoints to remediate broken object-level authorization, mass assignment, rate-limit bypasses, and JWT vulnerabilities.

Practical deliverables

  • Audit REST, GraphQL, and gRPC endpoints to remediate broken object-level authorization, mass assignment, rate-limit bypasses, and JWT vulnerabilities.
Capability 04

4. Network & Cloud Infrastructure Pentesting

Evaluate external perimeters, internal corporate networks, Active Directory, and multi-cloud environments to eliminate privilege escalation paths and exposed services.

Practical deliverables

  • Evaluate external perimeters, internal corporate networks, Active Directory, and multi-cloud environments to eliminate privilege escalation paths and exposed services.
Capability 05

5. Red Teaming & Adversary Simulation

Execute covert adversarial attack simulations mapped to MITRE ATT&CK tactics to benchmark and strengthen your SOC detection and response.

Practical deliverables

  • Execute covert adversarial attack simulations mapped to MITRE ATT&CK tactics to benchmark and strengthen your SOC detection and response.

Applied security workflows

Practical Vulnerability Assessment & Penetration Testing (VAPT) Use Cases

Common situations where security teams can apply this service to reduce exposure and improve day-to-day response.

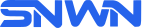
Security consultant discussing vulnerability findings with software developers
Built around your sectorEngineering For,
Vulnerability Assessment & Penetration Testing (VAPT)

Select a use case to view its scenario, outcome and delivery steps.

Use Case 01

Zero False-Positive Guarantee

Related: Security Consulting & Assessment →

Every detected security vulnerability undergoes rigorous manual validation with reproducible proof of concept evidence, eliminating false positives and remediation guesswork.

OutcomeEvery detected security vulnerability undergoes rigorous manual validation with reproducible proof of concept evidence, eliminating false positives and remediation guesswork.
  1. Assess

    Automated tools can produce long lists without showing which findings are exploitable.

  2. Plan

    Perform manual and automated penetration testing across web apps and SaaS platforms to uncover OWASP Top 10 and logic flaws.

  3. Apply

    Every detected security vulnerability undergoes rigorous manual validation with reproducible proof of concept evidence, eliminating false positives and remediation guesswork.

  4. Review

    Agree on systems, test windows, access needs, and rules of engagement.

Use Case 02

Critical Vulnerability Fast-Track

Related: Threat Detection & Response →

Receive immediate escalation within four hours upon our discovery of critical remote code execution or exposed sensitive database credentials.

OutcomeReceive immediate escalation within four hours upon our discovery of critical remote code execution or exposed sensitive database credentials.
  1. Assess

    Teams need help choosing which vulnerabilities to fix first.

  2. Plan

    Conduct static and dynamic security assessments of iOS and Android applications against OWASP MASTG standards, binary protections, and APIs.

  3. Apply

    Receive immediate escalation within four hours upon our discovery of critical remote code execution or exposed sensitive database credentials.

  4. Review

    Map the attack surface and run discovery and vulnerability checks.

Use Case 03

Comprehensive Retest Included

Related: Application & Infrastructure Security →

Every assessment includes complimentary post-remediation retesting to verify that your engineering team has effectively neutralized all reported technical exposures.

OutcomeEvery assessment includes complimentary post-remediation retesting to verify that your engineering team has effectively neutralized all reported technical exposures.
  1. Assess

    A fix may miss the root cause or affect another feature.

  2. Plan

    Audit REST, GraphQL, and gRPC endpoints to remediate broken object-level authorization, mass assignment, rate-limit bypasses, and JWT vulnerabilities.

  3. Apply

    Every assessment includes complimentary post-remediation retesting to verify that your engineering team has effectively neutralized all reported technical exposures.

  4. Review

    Validate priority findings and document evidence safely.

Delivery approach

How We Deliver Vulnerability Assessment & Penetration Testing (VAPT)

We agree on scope, work through each stage with your team, and share clear findings and next actions.

Select a step to explore its activities, buyer inputs and outputs.

  1. Step 01

    1. Scoping & Threat Modeling

    Agree on systems, test windows, access needs, and rules of engagement.
    Engineering Activities

    • Agree on systems, test windows, access needs, and rules of engagement.
    Buyer Inputs

    • Share relevant system details, stakeholder input, and access for this stage.

    Concrete Outputs

    • Documented findings and agreed next steps for 1. scoping & threat modeling.
  2. Step 02

    2. Reconnaissance & Surface Mapping

    Map the attack surface and run discovery and vulnerability checks.

    Engineering Activities

    • Map the attack surface and run discovery and vulnerability checks.

    Buyer Inputs

    • Share relevant system details, stakeholder input, and access for this stage.

    Concrete Outputs

    • Documented findings and agreed next steps for 2. reconnaissance & surface mapping.
  3. Step 03

    3. Vulnerability Analysis & Weaponization

    Validate priority findings and document evidence safely.

    Engineering Activities

    • Validate priority findings and document evidence safely.

    Buyer Inputs

    • Share relevant system details, stakeholder input, and access for this stage.

    Concrete Outputs

    • Documented findings and agreed next steps for 3. vulnerability analysis & weaponization.
  4. Step 04

    4. Exploitation & Post-Exploitation

    Deliver a report with severity, impact, and recommended fixes.

    Engineering Activities

    • Deliver a report with severity, impact, and recommended fixes.

    Buyer Inputs

    • Share relevant system details, stakeholder input, and access for this stage.

    Concrete Outputs

    • Documented findings and agreed next steps for 4. exploitation & post-exploitation.
  5. Step 05

    5. Remediation Briefing & Retesting

    Retest completed fixes and review remaining findings with your team.

    Engineering Activities

    • Retest completed fixes and review remaining findings with your team.

    Buyer Inputs

    • Share relevant system details, stakeholder input, and access for this stage.

    Concrete Outputs

    • Documented findings and agreed next steps for 5. remediation briefing & retesting.

Governance, scope & partnership

Keep Security Work Clear, Practical, and Accountable

We keep decisions and responsibilities visible so your team can understand what is in scope and what happens next.

Service scope and boundaries

Before work begins, we confirm the systems and environments in scope, access requirements, testing boundaries, reporting needs, and points of contact with your team.

Clear scope and ownership

Agree on the systems, people, and outcomes involved before work begins.

  • OSCP and CREST certified ethical penetration testers.
  • Zero false positive guarantee with reproducible exploits.

Practical technical guidance

Keep recommendations connected to your existing architecture and team capacity.

  • Sub four hour emergency alerts on vulnerabilities.
  • Complimentary post remediation retesting verifying complete fixes.

Visible progress and follow-up

Make findings easy to discuss and turn them into clear next steps.

  • Actionable developer friendly guidance accelerating patch deployment.

Security readiness checklist

Vulnerability Assessment & Penetration Testing (VAPT) Readiness Checklist

Use these checks to prepare for a useful review and identify the information your team may need to gather.

Security program & ownership

4 checks
  • Manual & Automated Deep-Dive Exploitation Testing
  • OWASP Top 10 & API Security Top 10 Verification
  • Cloud Infrastructure & Kubernetes Posture Audits
  • Red Teaming & MITRE ATT&CK Adversary Simulations

Platforms & protective controls

4 checks
  • Zero False-Positive Actionable PoC Proof Reports
  • Complimentary Retesting & Remediation Validation
  • PCI-DSS, ISO 27001, SOC 2 & HIPAA Audit Compliance
  • External Network Perimeter & Internal Pivot Testing

Response, evidence & improvement

4 checks
  • Mobile Application Security Testing (iOS & Android MAST)
  • Business Logic Flaw & Authorization Bypass Discovery
  • Active Directory & Kerberos Exploitation Analysis
  • Confidential NDA-Protected Executive Briefing

Common questions

Frequently Asked Questions - Vulnerability Assessment & Penetration Testing (VAPT)

Straightforward answers to help you understand the service and plan a next step.

Will penetration testing disrupt our production systems or degrade live user experience?

No. All penetration testing is conducted strictly according to customized Rules of Engagement (RoE) established during the scoping phase. Our certified ethical hackers utilize throttled bandwidth, non-destructive payloads, and off-peak scheduling when required to guarantee zero operational downtime or service interruption.

What is the difference between a Vulnerability Assessment and a Penetration Test?

A Vulnerability Assessment (VA) is a broad, automated scan that catalogs known potential vulnerabilities across your network. A Penetration Test (PT) goes much deeper: ethical hackers manually attempt to safely exploit those weaknesses, chain multiple vulnerabilities together, and demonstrate realistic business impact with verified Proof-of-Concept evidence.

How long does a typical VAPT engagement take, and what deliverables do we receive?

Most web application or network VAPT engagements take between 1 to 3 weeks depending on asset complexity and scope. You receive an Executive Summary outlining strategic risk for leadership, a Technical Finding Report with step-by-step developer remediation guidance, and a formal Attestation of Penetration Testing certificate for compliance auditors.

Do you offer free re-testing after our engineering team implements the patches?

Yes. Every SNWN VAPT engagement includes one complimentary round of remediation re-testing within 30 to 60 days of the initial report. We re-scan and manually verify the patched components to issue an updated, clean certification report.

Talk with a security specialist

Ready to Uncover Vulnerabilities Before Hackers Do?

Scope a VAPT assessment for your applications, APIs, cloud, or network environment.