A clean-energy trading platform running 60+ microservices faced three-week release bottlenecks because every update waited on manual security spreadsheet reviews. SNWN built standardized GitLab CI/CD templates with automated code scanning, Trivy container checks, cryptographic image signing, and Open Policy Agent guardrails for Terraform. Security approval time dropped by 80%, and zero critical misconfigurations reached production over 12 months.
When Manual Security Checks Bottleneck Fast-Moving Engineering
Utility customers required strict software supply-chain proof, including vulnerability reports and Software Bills of Materials (SBOMs) for every release. Doing those checks by hand right before release day frustrated both developers and security leads.
Key Operational Bottlenecks Before the Project
- Pre-release security sign-off took 10 to 15 business days per service update.
- Vulnerabilities found late in staging forced last-minute code rewrites and missed customer deadlines.
- Manual cloud console tweaks caused drift between staging and production firewall rules.
How We Shifted Security Left Into Every Pull Request
Instead of a slow manual gate at the end, we turned compliance rules into fast automated checks that run in five minutes whenever a developer pushes code.
Created Shared GitLab CI Templates Across All 60+ Microservices
We replaced 40 different handwritten pipeline files with three clean, versioned GitLab CI templates for Go, Python, and React services so every build runs the exact same security stages.
Added Secret Detection, SAST, and Automated Dependency Checks
Pull requests now scan automatically for hardcoded API keys, insecure code patterns, and vulnerable open-source packages - posting plain-English fix suggestions right inside the merge request.
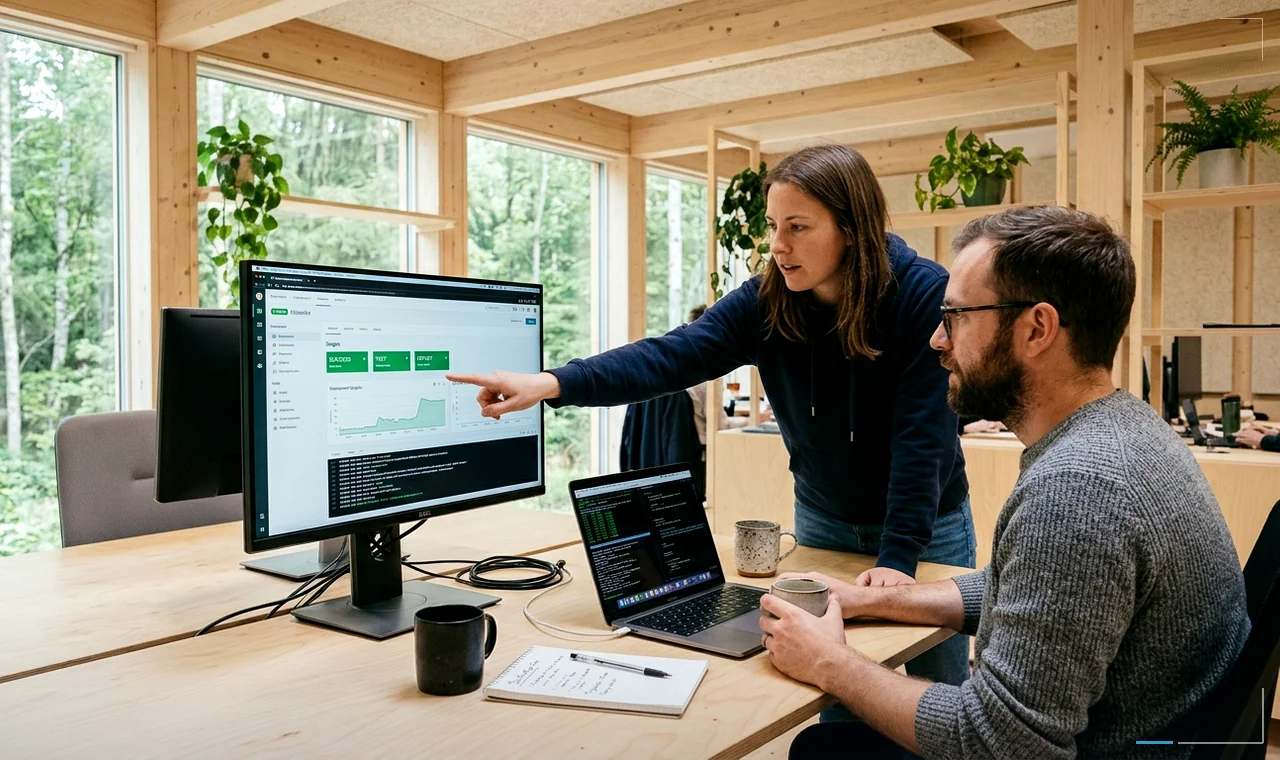
Enforced Container Signing and Automatic SBOM Generation
Every production Docker image is built from minimal distroless base images, scanned with Trivy, cataloged into a CycloneDX SBOM, and cryptographically signed with Cosign before Kubernetes will allow it to start.
Locked Down Cloud Changes with Terraform and Open Policy Agent
We blocked manual cloud console edits and added OPA policy checks to Terraform plans, automatically rejecting public S3 buckets, unencrypted disks, or overly wide security groups before deployment.
Faster Releases with Stronger Supply-Chain Proof
Developers now get security feedback in six minutes instead of two weeks, and utility auditors receive signed SBOM packages automatically with every release.
Shorter Release Lead Time
Security sign-off shrank from 12 days of manual review to automated pipeline checks.
Signed Production Containers
Kubernetes admission controllers block any unsigned or unscanned container image.
Production Cloud Misconfigurations
Zero high-severity infrastructure drift incidents across four quarters.
Day-to-Day Business Impact
- Engineering teams doubled feature delivery cadence for grid-bidding algorithms.
- Automated SBOM attachments helped win three new regulated European utility contracts.
- Security engineers shifted from spreadsheet chasing to threat modeling new product features.
Tools, Platforms, and Technologies Used
Every component in this deployment was selected for long-term stability, clear observability, and straightforward handover so internal engineers never get locked into black-box scripts.
CI/CD & DevSecOps Automation
See how our specialists design, migrate, and manage workloads like this every day.
Frequently Asked Questions About This Project
How much time do automated DevSecOps scans add to a CI/CD build?
By running SAST, secret scanning, and container checks in parallel with cached layers, total pipeline runtime increased by less than four minutes per commit.
What happens if an urgent zero-day vulnerability appears in a base library?
Because every deployed image has an indexed CycloneDX SBOM, the team can identify affected microservices in 30 seconds and roll out patched base images across all 60 services in under an hour.
Can OPA policy-as-code work with existing Terraform repositories?
Yes. OPA evaluates the JSON output of `terraform plan` right inside CI without requiring you to rewrite your existing Terraform modules from scratch.