A growing payment gateway needed to pass PCI-DSS 4.0 and SOC 2 Type II audits to onboard enterprise bank partners, but its engineering team was buried under 2,000 noisy cloud alerts a day. SNWN segmented the cardholder environment using zero-trust policies, ran full-stack VAPT remediation, and staffed a 24/7 Managed SOC with automated SOAR containment. The company passed both audits with zero critical findings and cut threat containment time by 78%.
Why Fast Growth Created Security and Audit Pressure
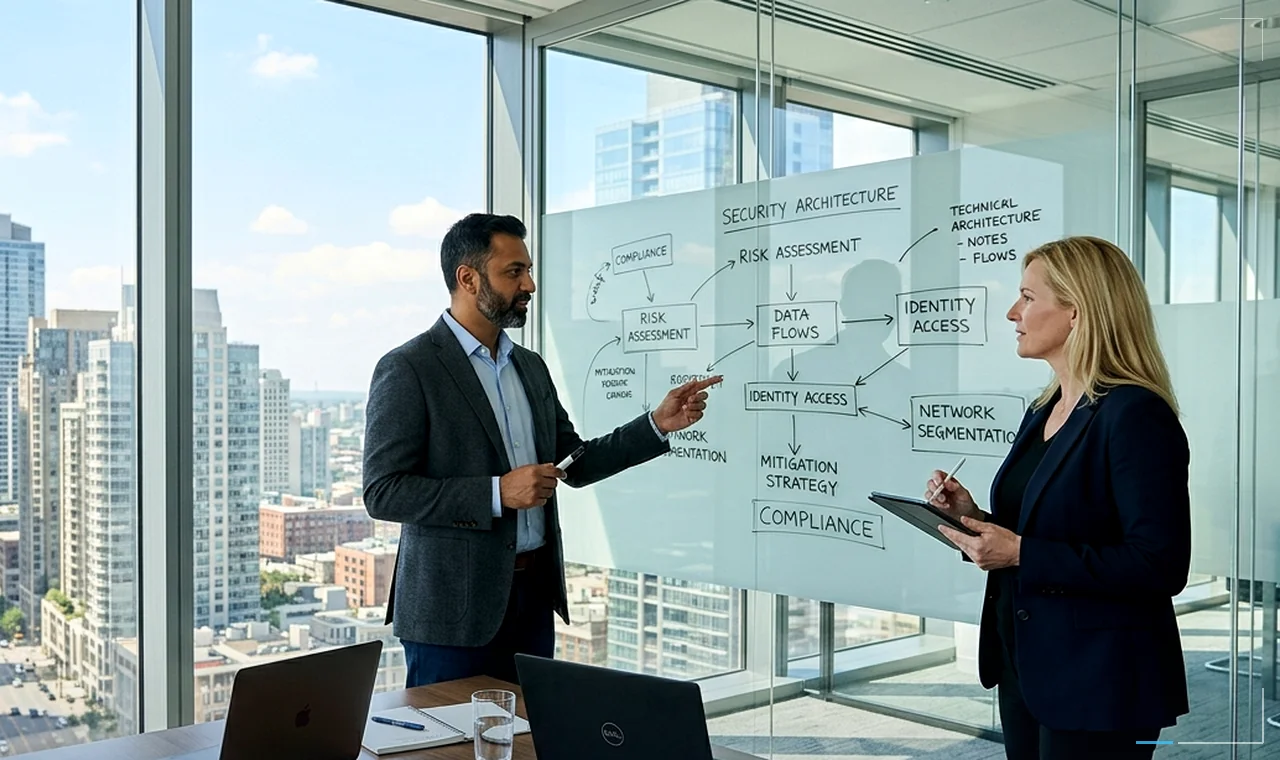
When two tier-one banking partners asked for current PCI-DSS 4.0 and SOC 2 Type II attestations before signing commercial contracts, the client realized their startup-era cloud setup had too many shared permissions and unmonitored logs.
Key Operational Bottlenecks Before the Project
- Developers shared broad cloud IAM roles across staging and production accounts, creating audit blockers.
- Default cloud security tools generated over 2,000 raw alerts daily, hiding real anomalies in false positives.
- No dedicated night or weekend security analysts were watching API credential abuse or WAF spikes.
How We Built Zero-Trust Controls and 24/7 SOC Coverage
We worked side by side with the client's backend engineers so stronger security never slowed down weekly product releases.
Isolated the Cardholder Data Environment (CDE)
First, we carved out a dedicated, locked-down VPC exclusively for payment tokenization and settlement services. Everything outside that boundary talked only to tokenized IDs, shrinking PCI-DSS audit scope by more than half.
Replaced Standing Admin Keys with Just-in-Time Zero-Trust IAM
We removed long-lived SSH keys and static cloud access tokens. Engineers now request temporary, time-boxed production access tied to hardware MFA and SSO, with every command logged automatically.
Ran VAPT Penetration Testing and Hardened APIs
Our offensive security specialists tested every external API, webhook endpoint, and container image. Together with the dev team, we patched rate-limit gaps, enforced strict mTLS between microservices, and tuned Web Application Firewall rules.
Connected Logs to SNWN's 24/7 Managed SOC and Automated Evidence
We routed cloud, Kubernetes, database, and WAF telemetry into a unified SIEM/SOAR pipeline. Tuned correlation rules cut false positives by 91%, while automated scripts collect daily compliance evidence directly for auditors.
Security Outcomes That Unlocked Enterprise Revenue
Instead of treating compliance as a last-minute scramble, security became a repeatable part of daily operations - helping close two major bank partnerships.
Critical Audit Findings
Cleared both PCI-DSS 4.0 and SOC 2 Type II external assessments on the first pass.
Faster Threat Containment
Automated SOAR playbooks block suspicious IPs and revoke tokens in under 3 minutes.
Less Alert Noise
Tuned SIEM rules eliminated repetitive false alarms so analysts focus on real threats.
Day-to-Day Business Impact
- Signed two enterprise banking partnerships within 30 days of receiving PCI-DSS attestation.
- Cut auditor evidence preparation time from four weeks of engineer spreadsheets to two days.
- 24/7 Managed SOC analysts now review every high-severity anomaly within 10 minutes, day or night.
Tools, Platforms, and Technologies Used
Every component in this deployment was selected for long-term stability, clear observability, and straightforward handover so internal engineers never get locked into black-box scripts.
Cybersecurity & Managed SOC
See how our specialists design, migrate, and manage workloads like this every day.
Frequently Asked Questions About This Project
How does isolating the Cardholder Data Environment speed up PCI-DSS compliance?
By keeping raw card numbers inside a small, strictly segmented tokenization VPC, the rest of your application servers never touch card data - reducing the number of systems auditors must inspect by 50% to 70%.
Will zero-trust IAM slow down developers during production debugging?
No. Developers still get read-only observability logs instantly, and when elevated access is needed for an incident, Slack-integrated approval grants a temporary session in under 60 seconds.
What is included in SNWN's 24/7 Managed SOC service?
We provide continuous log ingestion, custom SIEM detection rules, automated SOAR containment playbooks, human L2/L3 threat hunting 24/7/365, and monthly compliance posture reports.